
AI-Enhanced Zero-Trust
AI-enhanced zero-trust adapts access decisions to context in real time. See how adaptive access controls will become essential for scaling SaaS platforms.



AI-Enhanced Zero-Trust
The Next Phase of Zero-Trust Challenges
A large portion of recent breaches involved misused credentials, which is exactly what "never trust, always verify" is meant to stop. AI extends that principle by reading context, things like device health and login behavior, and blocking anomalies as they happen rather than after a report runs the next morning.
AI's Role in Advanced Access Controls
The core idea is risk-based authentication. Machine learning scores each login attempt and flags the ones that do not fit a user's normal pattern, an unfamiliar device, an odd location, an unusual time. That cuts incident response from days to minutes and helps you keep up with new compliance requirements. We have seen this approach catch an API exploit attempt that a static policy would have waved through.
Data Table


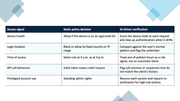
The left column is the same in both models; what changes is that the decision is made per request, using context, instead of once at policy-writing time.
When you don't need this
AI-driven verification is a layer on top of identity and access management, not a replacement for it. If you cannot list every admin account, every service account and every third-party integration with access to production, you are not ready for adaptive scoring. Fix the inventory, enforce MFA everywhere, remove standing privilege and turn on the logging you already pay for. Those steps stop most credential misuse on their own.
You also do not need it if your environment is small and stable: a team of ten, one cloud provider, a handful of SaaS tools and no customer-facing API. Conditional access rules in your existing identity provider will cover you, and a behavioural model has too little history to learn from anyway.
Revisit the question when you have a growing external API surface, contractors and vendors with production access, or a compliance driver such as SOC 2 compliance or ISO 27001 that asks you to show continuous monitoring of access. At that point the extra context starts paying for itself.
Steps to Evolve Your Zero-Trust Strategy
Start by mapping gaps in your identity and access management. From there, add AI-driven verification on top of tools you likely already run, such as Okta with its machine learning add-ons. Roll it out gradually, beginning with your highest-risk surfaces like admin and privileged accounts. Then track real numbers, such as reduced breach attempts, so you can show the work is paying off.
Getting this right is an ongoing effort, and good guidance makes the difference between adopting AI cautiously and adopting it well. If zero-trust is on your roadmap, our Virtual CISO Services can help fold it into your broader security strategy.
Conclusion
Start with a free CIS Controls gap assessment to identify gaps in identity and access management and evolve your Zero-Trust Strategy (CIS Controls 5 and 6 cover account and access control management).
Related Articles


What Is Context Engineering?


Claude Cowork: AI Security Risks


Hybrid Human-AI Security Teams


Navigating Future AI Regulations


Generative AI Cybersecurity Risks


Security Risks of Autonomous Agents
Our Industry Certifications
Our diverse industry experience and expertise in AI, Cybersecurity & Information Risk Management, Data Governance, Privacy and Data Protection Regulatory Compliance is endorsed by leading educational and industry certifications for the quality, value and cost-effective products and services we deliver to our clients.



We specialize in transforming scaling SMB's, Startups, SaaS businesses in regulated industries into cyber-resilient organizations with cost-effective Virtual / Fractional CISO & AI Governance Services.


Awards & Recognition


