Table of Contents
- What is Shadow AI?
- How common is Shadow AI in 2026?
- Why Shadow AI is a business risk, not just an IT problem
- Where the damage actually shows up
- Shadow AI vs Sanctioned AI: What actually differs
- Why banning AI does not work
- How to get Shadow AI under control: a 30/60/90-day plan
- When you do not need a formal Shadow AI programme
- Where IRM can help
Date Published: September 23, 2026
What Is Shadow AI?
Your team is already using AI.
The question is whether you know which tools, and what data they are feeding them.
Every few weeks we get the same call. A founder is filling in an enterprise customer's security questionnaire, reaches the question "List all AI tools that process customer data," and realises nobody in the company can answer it. Not the CTO, not ops, not the person who owns the vendor list. That gap has a name: shadow AI.
What is Shadow AI?
Shadow AI is the use of artificial intelligence tools, models or features inside an organisation without the knowledge, approval or oversight of the people responsible for security, privacy and risk. It includes a sales rep pasting call notes into a free chatbot, a developer sending proprietary code to an AI coding assistant on a personal account, a marketer uploading a customer list to an AI analytics tool, and an AI feature quietly switched on inside software you already pay for.
It is the direct descendant of shadow IT, the Dropbox and personal Gmail problem of the 2010s. The difference is what the tool does with the data. A file-sharing app stores what you give it. An AI tool reads it, reasons over it, may retain it, and in some consumer tiers may use it to improve future models, depending on account settings.
In 2026, shadow AI also comes in forms that are easy to miss. AI meeting bots join calls and record customers. Browser extensions read every page an employee opens. AI agents connected to email, calendars and drives can act on data, not just read it. Across our assessments, these three categories are the ones most often absent from a company's vendor list, because nobody thought of them as "buying software."
How common is Shadow AI in 2026?
Very. Microsoft and LinkedIn's 2024 Work Trend Index found that 75% of knowledge workers already used generative AI at work, and 78% of those AI users brought their own tools rather than waiting for company-approved ones. At small and medium-sized companies the figure was 80%. Just as telling, 52% of AI users said they were reluctant to admit using AI for their most important tasks.
Read those two numbers together. Most of your team is using AI, and half of them would rather you did not ask about it. That is not a discipline problem. It is a signal that the approved path is slower than the unapproved one.
Why Shadow AI is a business risk, not just an IT problem
IBM's 2026 Cost of a Data Breach Report, conducted by the Ponemon Institute across 602 organisations breached between March 2025 and February 2026, put hard numbers on it:
43% of breached organisations studied reported a security incident involving shadow AI, up from 20% a year earlier.
Those incidents averaged $5.39 million, against a global average breach cost of $4.99 million.
68% of breached organisations lacked AI governance to manage AI or detect shadow AI, either with no policy or with one still being written.
Only 38% required IT approval before AI tools were deployed, down from 45%.
Usage doubled. Control shrank. For a 60-person SaaS company, the multimillion-dollar average is less relevant than what sits behind it: the specific ways shadow AI hurts a business your size. For our full breakdown of the IBM findings and the EU AI Act timeline, read Shadow AI in 43% of AI Breaches.
Where the damage actually shows up
Data leakage. Customer records, source code, contracts and pricing leave your environment with no contract governing what happens next. Samsung learned this publicly in 2023, when engineers reportedly entered confidential source code into ChatGPT and the company restricted generative AI on its devices and networks.
Privacy non-compliance. In Canada, PIPEDA Principle 4.1.3 keeps you responsible for personal information you transfer to a third party for processing. Under Quebec's private-sector privacy act, as amended by Law 25, you need a privacy impact assessment and a written agreement before personal information leaves Quebec. GDPR Article 28 requires a binding contract with every processor. An employee's free AI account satisfies none of these.
Lost deals. Enterprise buyers now ask about AI use in security reviews. "We don't know" stalls a procurement cycle faster than almost any technical finding.
Bad decisions on bad output. Unvetted tools produce unvetted answers. Nobody checked the model, the prompt, or whether the output was reviewed before it reached a customer.
Shadow AI vs Sanctioned AI: What actually differs
The tool is often the same. The controls around it are not. This is the comparison we walk clients through, and yes, it carries an opinion.
Control | Shadow AI | Sanctioned AI |
|---|---|---|
Who approved it | Nobody | Named owner, recorded decision |
Data agreement | Consumer terms of service | Business terms, DPA, training opt-out |
Identity | Personal email, no SSO | Company SSO, offboarded with the employee |
Data allowed in | Whatever the user pastes | Defined by classification level |
Visibility | None | Inventory, logs, periodic review |
Our view | Banning it outright usually makes it worse | The goal: make this the easier path |
Why banning AI does not work
The instinct is to block ChatGPT at the firewall and send a stern email. We have watched this fail repeatedly. Employees switch to their phones, personal laptops or a different tool the block list has not caught yet. The usage continues. You just lose the last bit of visibility you had.
Shadow AI is a demand signal. People reach for these tools because they save hours. The fix is to meet that demand with an approved option and clear rules, then govern it.
How to get Shadow AI under control: a 30/60/90-day plan
This is the order of operations we use with small and mid-sized clients. It assumes no dedicated security team.
Days 1 to 30: Find it
Run an anonymous, no-blame survey: which AI tools do you use, for what, with what data?
Review SSO logs, expense reports and browser extension lists for AI services.
Check your existing SaaS vendors for AI features switched on by default.
Build a single AI inventory: tool, owner, data types, account type, contract status.
Days 31 to 60: Decide and write it down
Classify each tool: approved, approved with restrictions, or retired.
Publish a one-page AI acceptable use policy. Plain language, with examples of what never goes into an AI tool.
Move approved tools onto business tiers with data processing agreements, training opt-outs and SSO.
Add AI questions to your vendor risk review so new tools enter through the front door.
Days 61 to 90: Make it sustainable
Stand up a lightweight request process with a target turnaround of days, not weeks.
Train staff on the policy with real examples from your own survey.
Map controls to a recognised framework such as the NIST AI Risk Management Framework or ISO/IEC 42001.
Schedule a quarterly inventory refresh. Shadow AI is not a one-time clean-up.
A slow approval process is the single biggest cause of shadow AI we see. If your request process takes a month, you have designed shadow AI into the company.
When you do not need a formal Shadow AI programme
Not every company needs the full plan tomorrow. If you have fewer than 15 people, handle no regulated or customer personal data, and have no enterprise customers asking about AI, a short policy and a shared list of approved tools is a proportionate start. Spending more than that would be over-engineering.
The moment any of the following is true, the calculus changes: you process personal information for Canadian, Quebec, US or EU customers; you are pursuing SOC2, ISO 27001 or ISO 42001; you sell to enterprises; or your product itself uses AI. At that point, shadow AI is a finding waiting to appear in an audit or a questionnaire.
And be clear about what governance does not do. An AI policy will not stop a determined insider, and an inventory is only as good as its last refresh. The aim is visibility and accountability, not zero risk.
Where IRM can help
Most companies we work with do not need a full-time CISO to fix this. They need someone to run the inventory, write a policy people will actually follow, and connect it to the frameworks their customers ask about. That is what our AI-native vCISO service does, alongside our AI governance and ISO 42001 readiness work and data security and privacy programmes.
If you want a starting point, our free ISO 42001 Gap Assessment and AI Governance Playbook will show you where you stand in under an hour. Our process, risk and controls work turns the findings into repeatable controls, and our transparent pricing starts from $2,000 per month.
Or skip straight to the conversation. Book a consultation and bring your answer to one question: which AI tools touched customer data in your company last week?
Related Articles


AI Safeguards vs AI Guardrails

How to Protect Data Privacy

Shadow AI in 43% of AI Breaches

AI Agent Cyberattack


The Plumbing Behind AI Agents

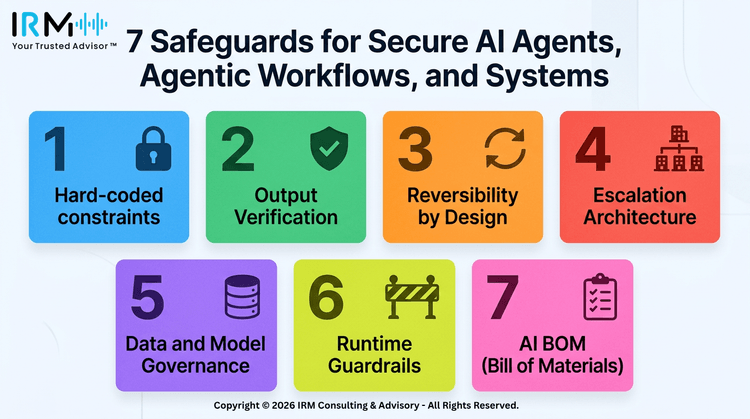
7 Safeguards to Secure AI Agents
Our Industry Certifications
Our diverse industry experience and expertise in AI, Cybersecurity & Information Risk Management, Data Governance, Privacy and Data Protection Regulatory Compliance is endorsed by leading educational and industry certifications for the quality, value and cost-effective products and services we deliver to our clients.


We specialize in transforming scaling SMB's, Startups, SaaS businesses in regulated industries into cyber-resilient organizations with cost-effective Virtual / Fractional CISO & AI Governance Services.


Awards & Recognition


